

September 22, 2026 The FDA Now Requires Imaging Devices to Be Cyber-Secure by Design. Here Is How to Make It Your Purchasing Checklist.
When your practice buys a new cone-beam CT unit, an intraoral sensor or a chairside scanner, the questions in the room are predictable: image quality, workflow, price, service contract. There is one question almost no one asks – and since 2023, U.S. federal law has quietly made it a fair one. The manufacturer of that connected device now has a legal duty to build cybersecurity into it and prove that to the FDA before it can be sold. You paid for that work. You are entitled to see it. Most practices never think to look.
This is not a breach alert and there is nothing to patch this morning. It is something more useful: a durable rule you can turn into leverage at the exact moment you have the most of it – before you sign the purchase order.
What the law actually requires
In December 2022, Congress added Section 524B to the Food, Drug, and Cosmetic Act, and it took effect in March 2023. It applies to “cyber devices” – broadly, any device that includes software and can connect to the internet or a network, which covers essentially every modern digital imaging system in a dental office. To win FDA clearance, the maker must now do several things and document them in the premarket submission:
- Design, develop and maintain the device to be reasonably cyber-secure – so-called secure by design, rather than security added after the fact.
- Provide a plan to monitor, identify and address post-market vulnerabilities, including issuing patches on a reasonable cadence and out-of-cycle for critical flaws.
- Publish a coordinated vulnerability disclosure process, so researchers have a legitimate way to report problems.
- Provide a Software Bill of Materials (SBOM) – a machine-readable inventory of the software components inside the device, including the open-source libraries it depends on.
The FDA has been willing to refuse submissions that fail to include this material since late 2023. In 2026 the guidance was refreshed to line up with the agency’s new Quality Management System Regulation (QMSR), which folds these expectations into the manufacturer’s overall quality system. The headline for a buyer is unchanged and worth repeating: the SBOM and cybersecurity requirements did not loosen. They are the baseline now.
Why a dental practice should care about a manufacturing rule
Because the burden of a device’s flaws does not stay with the manufacturer. It lands on the practice that owns the device, holds the patient records it touches, and answers to patients and to PHIPA when something goes wrong. We have written before about how imaging hardware becomes a security question the moment it joins your network – from where a sensor was made and what it quietly talks to, to the awkward reality of keeping an older scanner or CBCT running safely after the vendor stops patching it.
Section 524B attacks that problem at the source. A device built to the standard is one whose maker has committed, on the record, to shipping patches and telling you about vulnerabilities for the life of the product. A device that predates or ignores the standard is one where you are on your own. The difference between those two purchases is invisible on the spec sheet and enormous over the eight-to-ten years the equipment will sit in your operatory.
The one document that changes your leverage: the SBOM
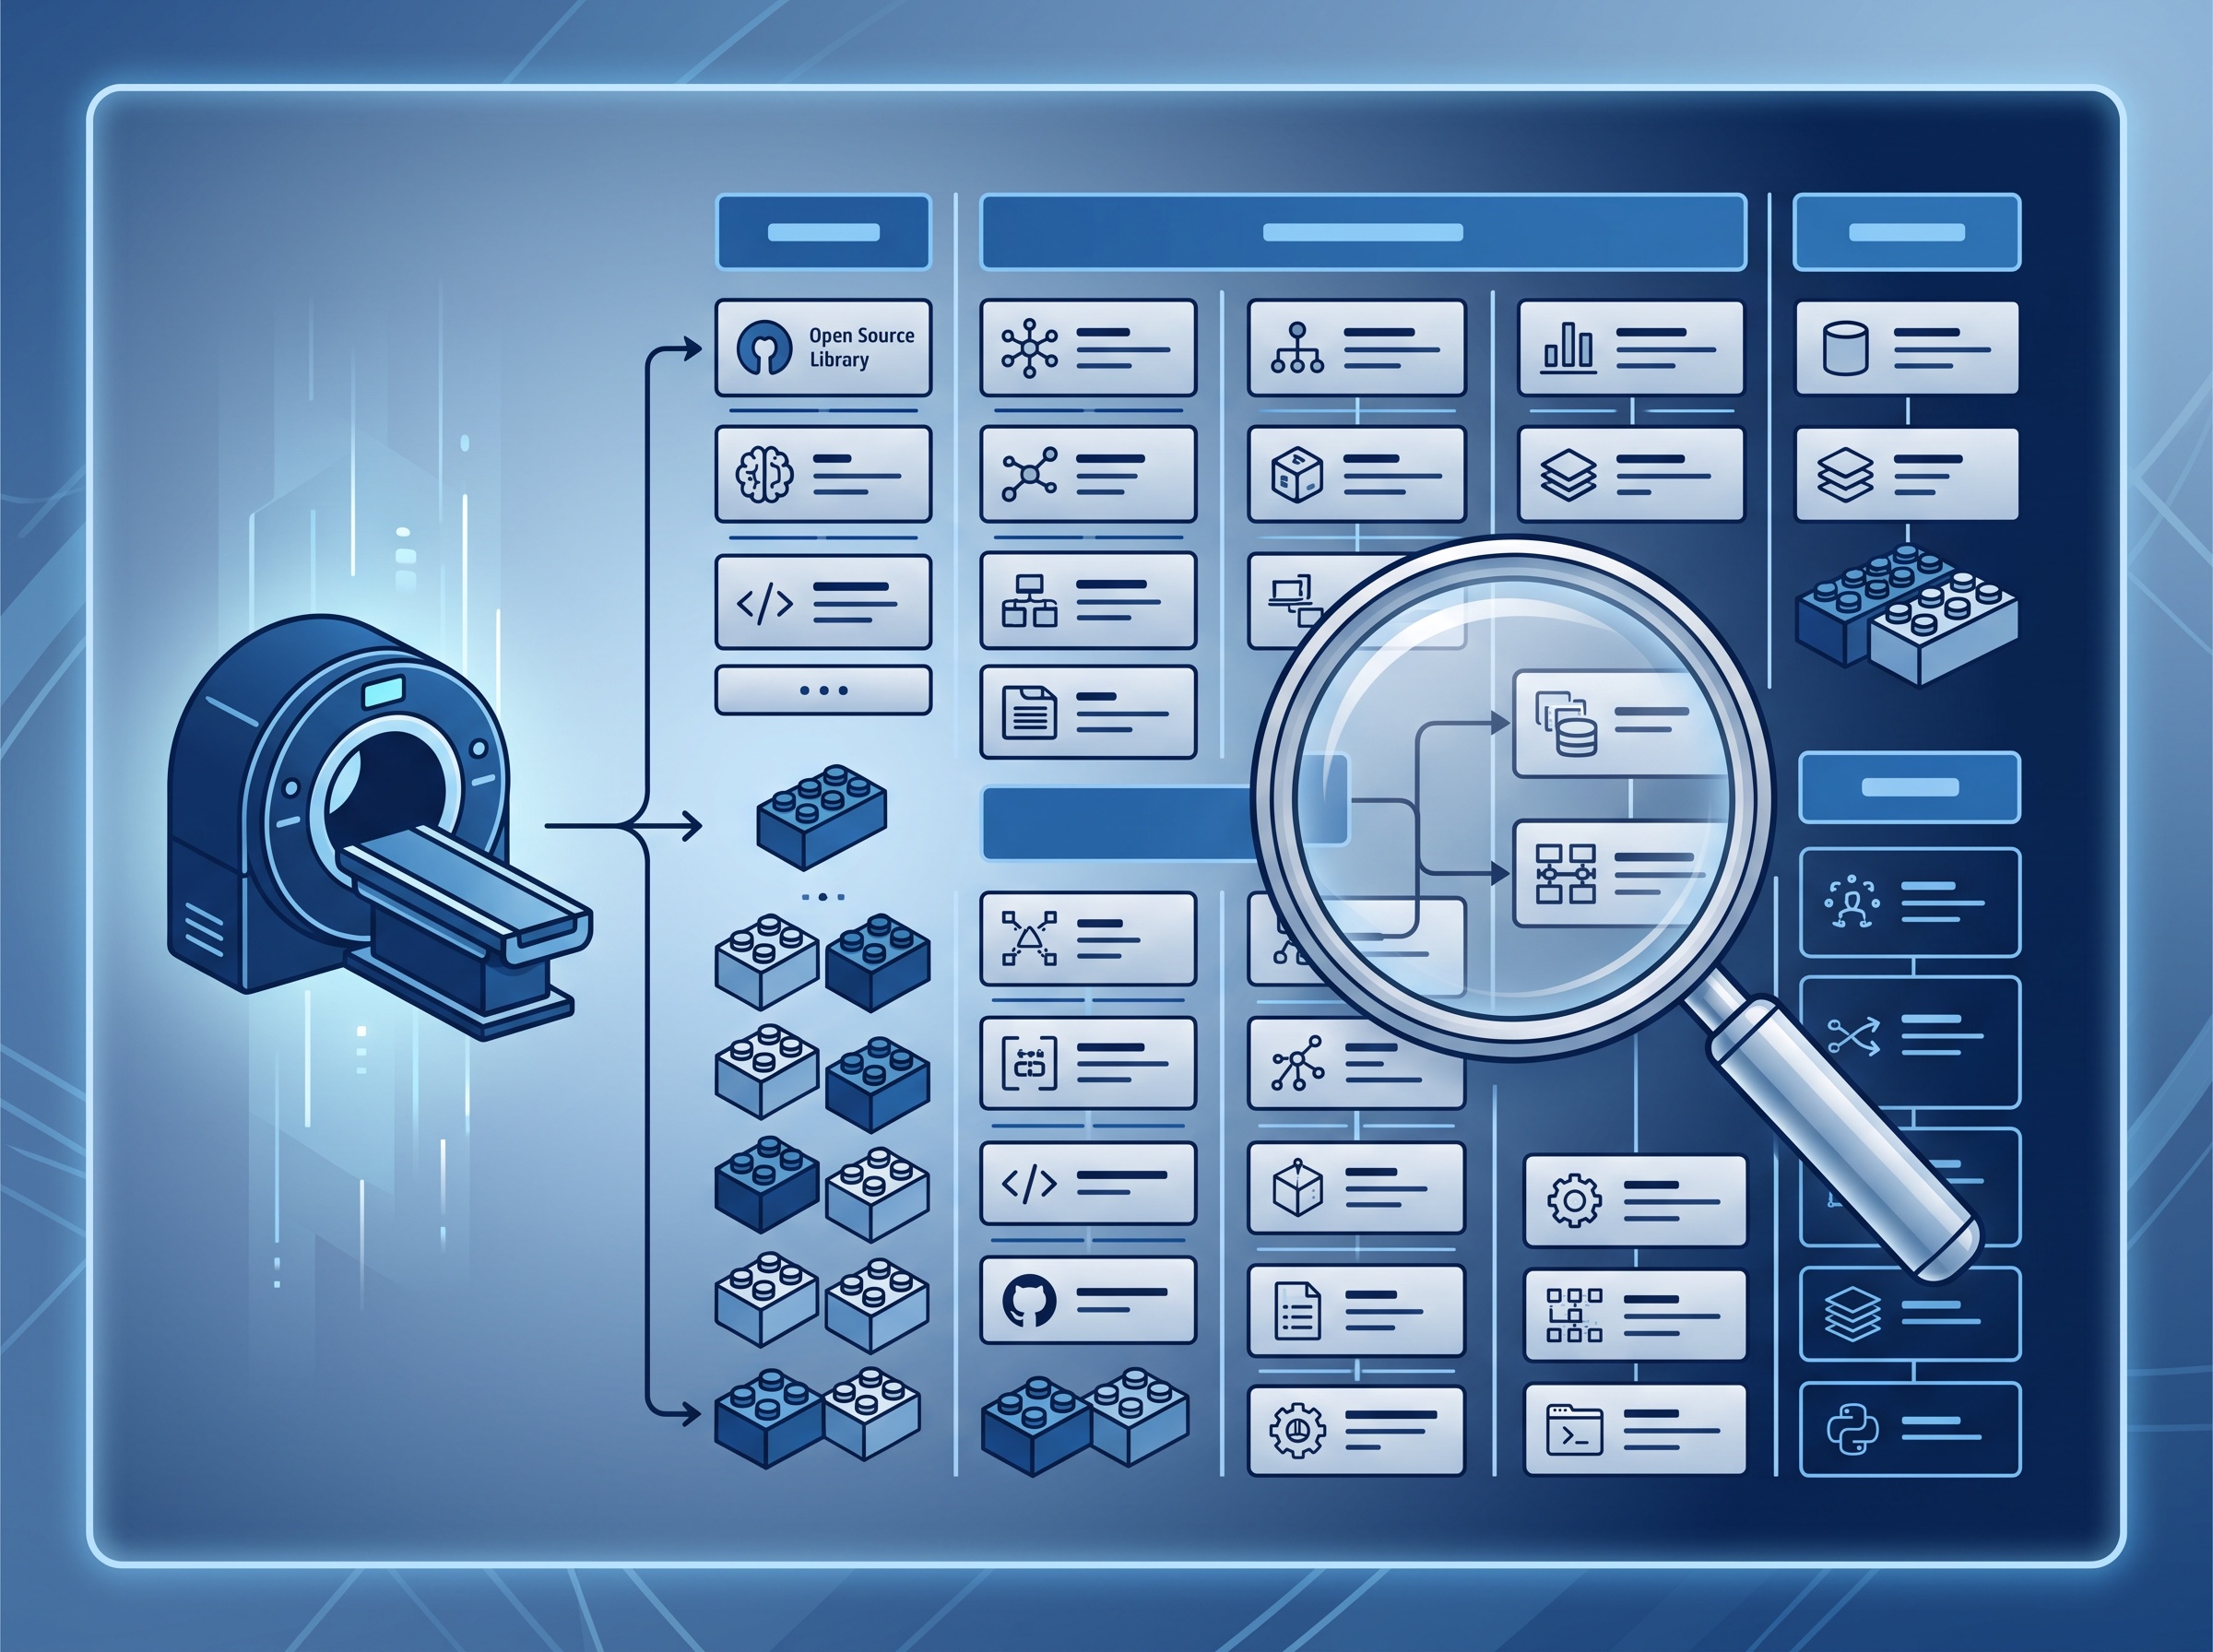
Of everything in the rule, the SBOM is the piece a practice can use directly. Think of it as an ingredients list for the device’s software. Modern imaging systems are assembled from dozens of third-party and open-source components you never chose and cannot see – and those components are where a growing share of critical vulnerabilities live. When one of them makes the news, the first question is always the same: do we run it?
Without an SBOM, answering that means waiting on the vendor’s goodwill and hoping they respond before an attacker does. With one, you – or the IT partner who manages your network – can check in minutes whether the flawed component is inside your scanner. That is the same discipline that turned a recent scramble over a buried software flaw into a five-minute lookup for practices that knew what they were running. The SBOM is what makes “know what you run” possible for a sealed medical device.
Turn the rule into three purchasing questions

You do not need to read an FDA submission or become a compliance expert. You need to make three requests part of every imaging-equipment evaluation, and treat a vague answer as the answer:
- “Please provide the SBOM for this device.” A vendor building to the standard has one ready. Hesitation, confusion or a promise to “look into it” tells you where cybersecurity sits on their priority list.
- “What is your patching commitment and your end-of-support date?” Get the cadence for routine and emergency updates, and the year support ends, in writing. This is the single most valuable fact for planning, because the device will outlive its support window and you need to know when.
- “How do I report a security problem, and how will you notify me of one?” A real coordinated-disclosure process and a defined customer-notification path separate a serious manufacturer from one that will go quiet the day a flaw surfaces.

None of this slows a purchase you were going to make anyway. It simply ensures that when two units are close on price and image quality – the situation you are usually in – the tiebreaker is the one that will cost you the least grief three years from now. It also pairs naturally with the questions you should already be asking about how a new device connects to your network, the same due diligence we applied when the FDA cleared AI that reads 3D dental scans and when a widely used imaging server flaw showed why a PACS should never face the internet.
What to do this week
Nothing here is urgent, and that is the point – it is far cheaper to build this into how you buy than to retrofit it after an incident. If you have a device purchase on the horizon, add the three questions above to your evaluation. If your existing fleet is a mystery, start a simple inventory: what each connected imaging device is, what it runs, when its support ends, and whether the vendor can supply an SBOM. That list is the foundation of every good decision that follows.
At Compudent Systems we help dental practices across the GTA and Ontario vet imaging and IT equipment before it is purchased, inventory what is already on the network, and build the segmentation and monitoring that keep it all safe for its full service life. If you have a device on order – or a fleet you have never fully mapped – contact Compudent Systems for an assessment. The best time to ask these questions is before the invoice is paid.
Sources & further reading:
- FDA – Cybersecurity in Medical Devices: Quality Management System Considerations and Content of Premarket Submissions
- Interlynk – FDA SBOM Requirements for Medical Devices: The Complete 2026 Guide
- Censinet – FDA Cybersecurity Guidance: Medical Device Reporting Rules
Related Reading
- Where Was Your Imaging Sensor Made, and What Is It Talking To? Device Provenance Is Now a Dental Practice Security Question
- You Can’t Patch That Old Sensor or CBCT: How to Safely Keep Legacy Imaging Devices on Your Dental Network
- One Screen for Scans and X-Rays: What Medit’s AuraVue With Overjet AI Means for Your Dental Practice