
September 23, 2026 September’s Windows Updates Are Breaking Always On VPN: What Practices With Remote Access Need to Check Now
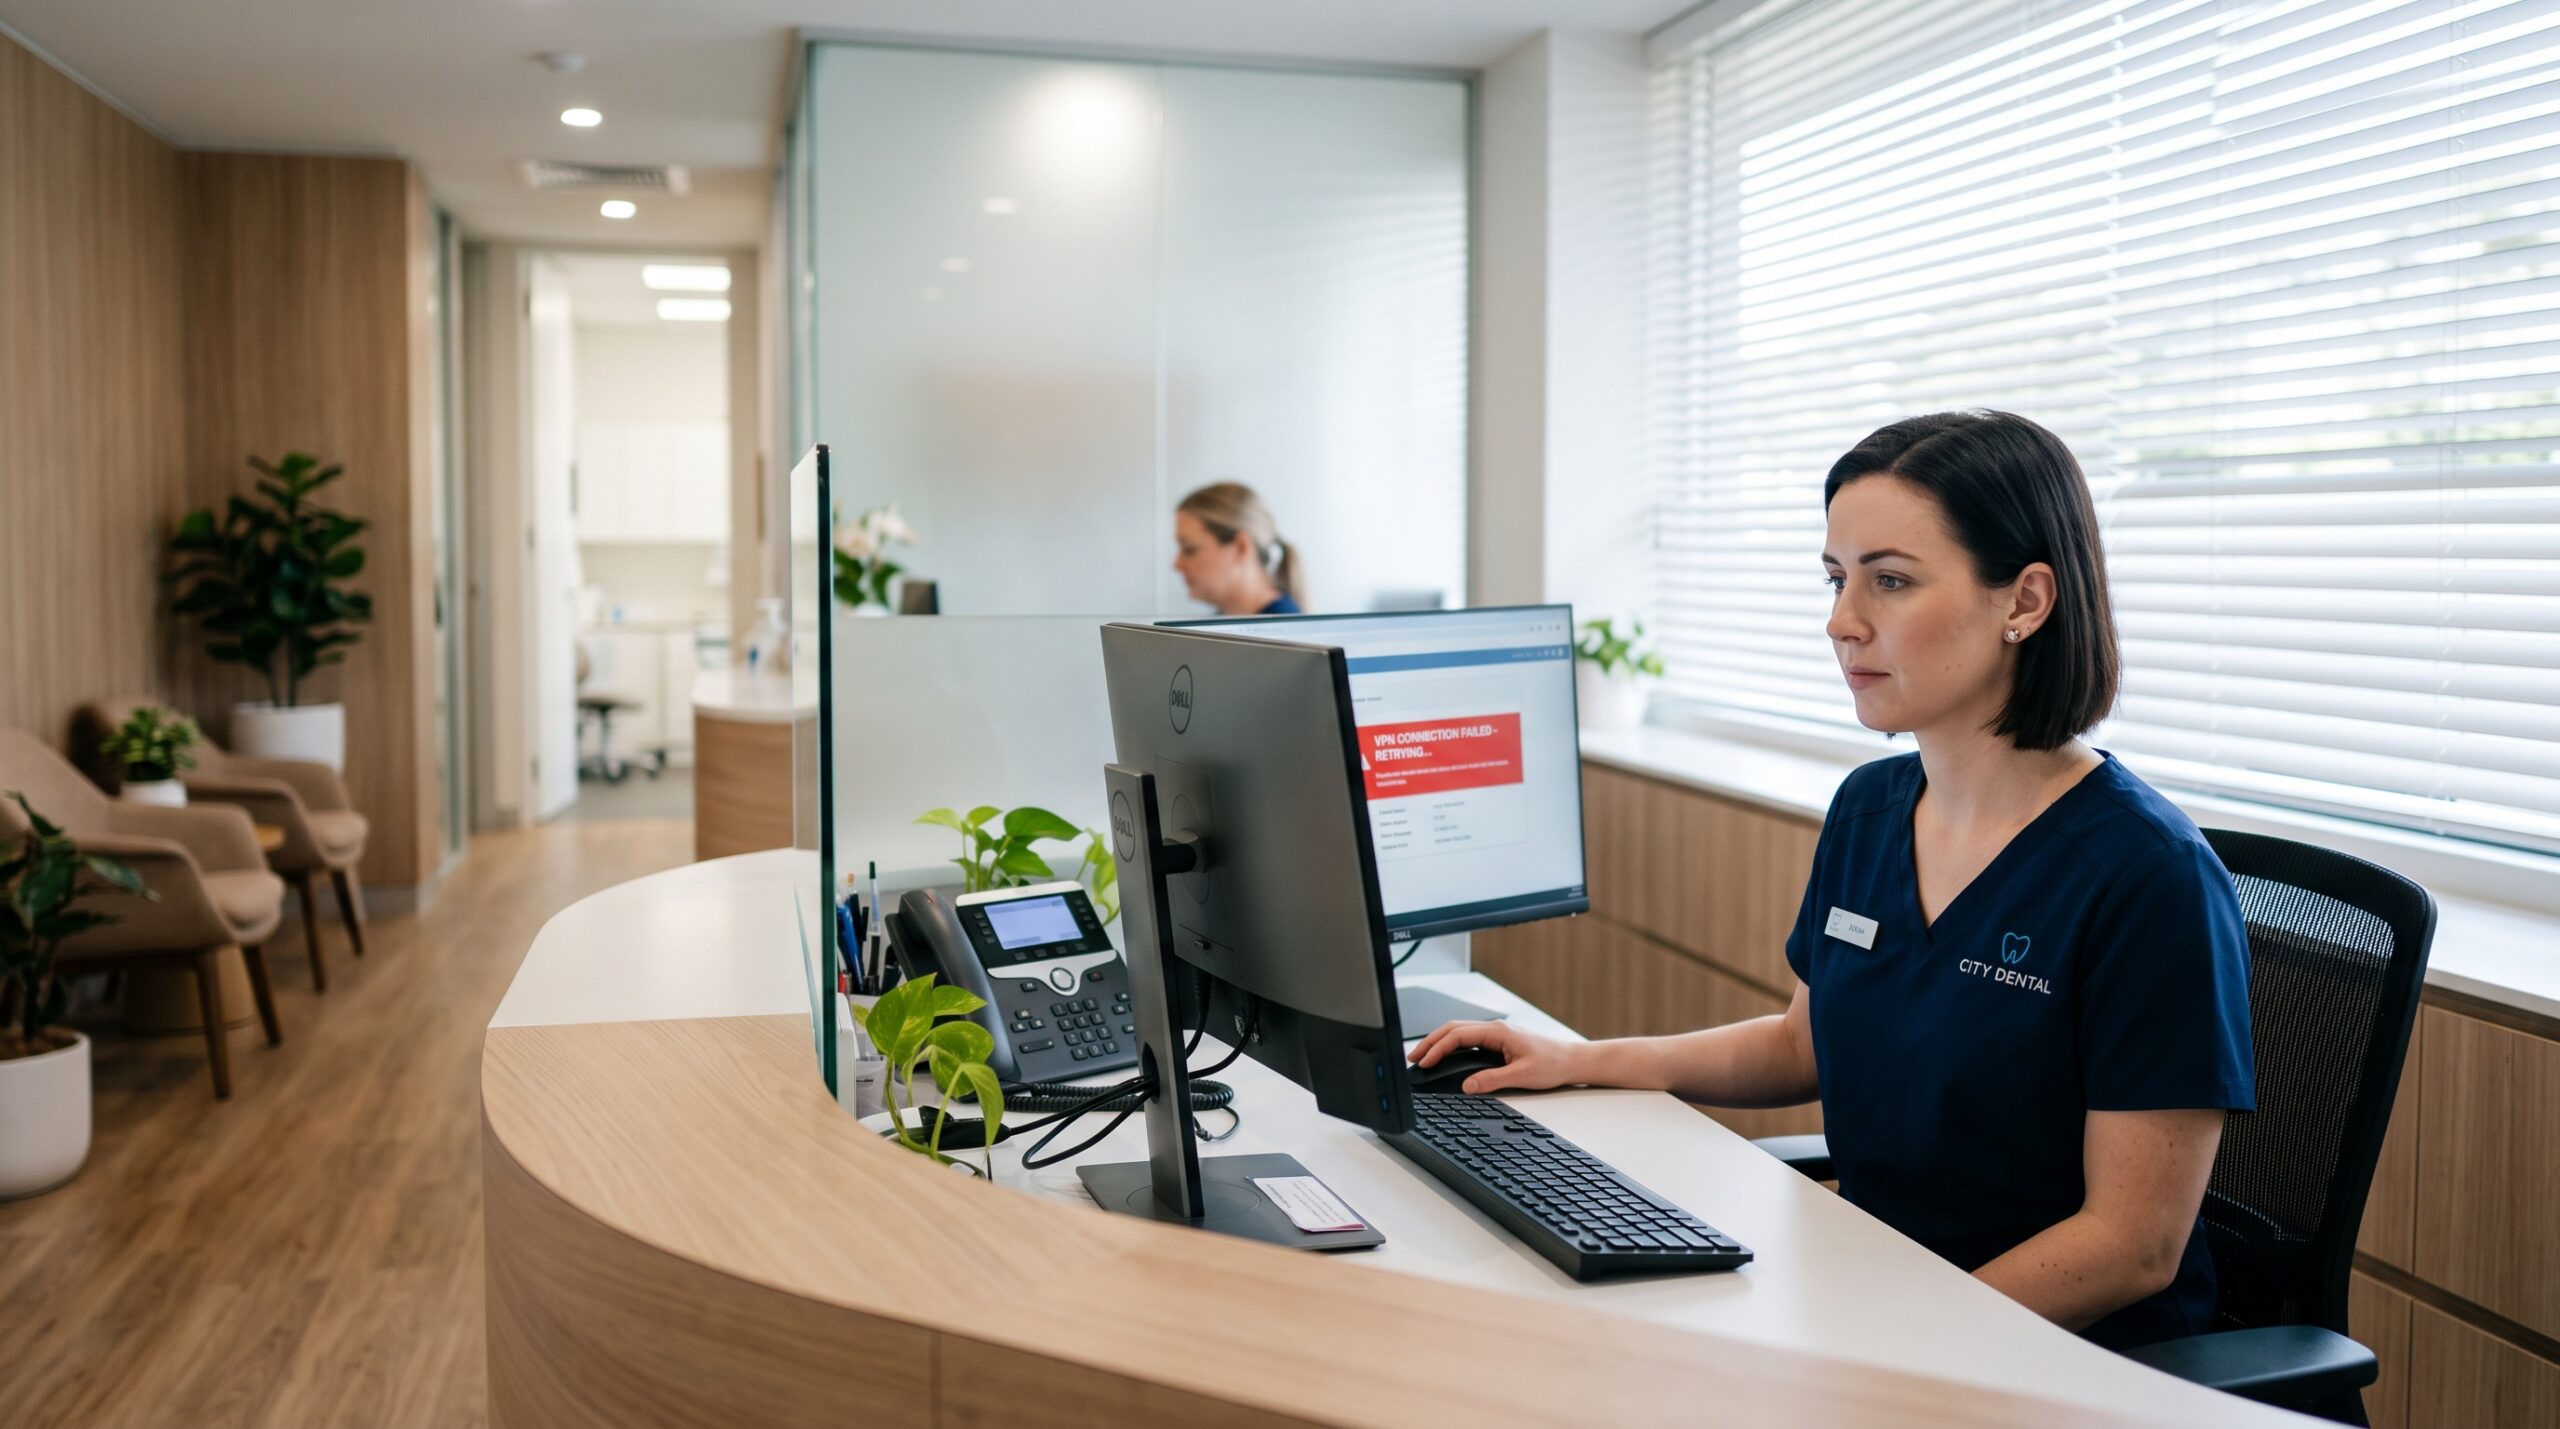
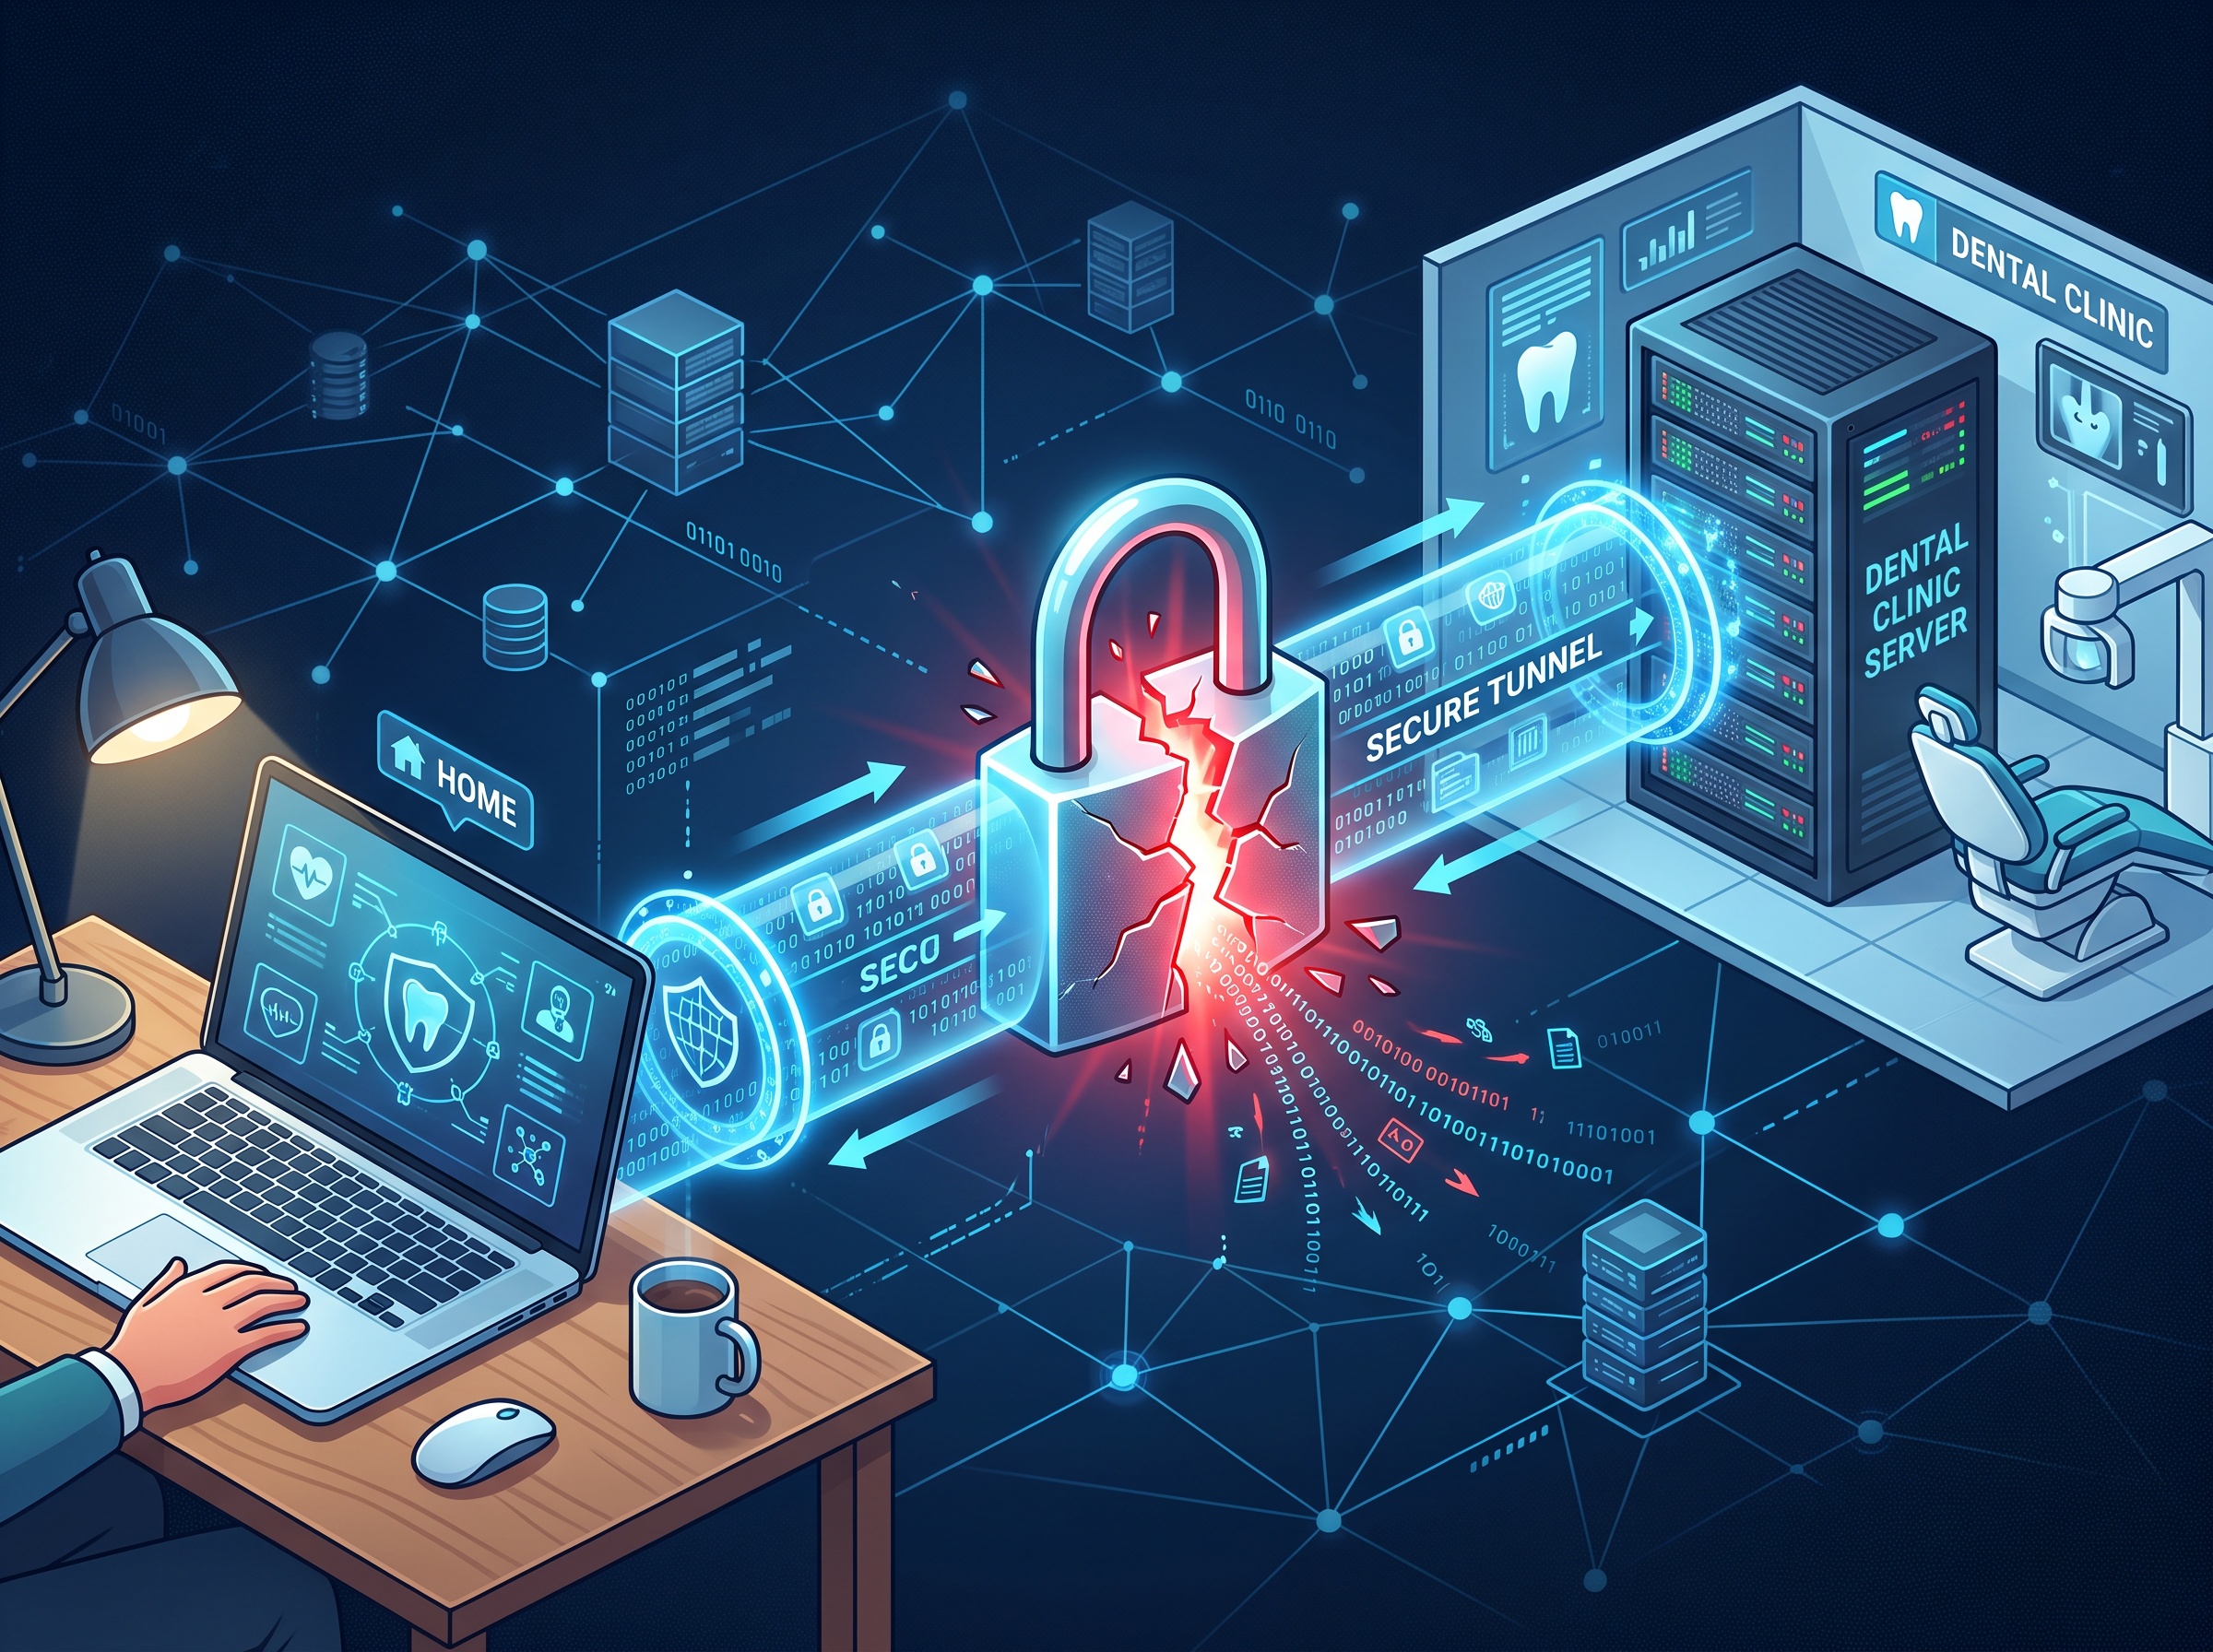
If a team member who normally works from home or a satellite operatory suddenly can’t reach your practice server this week, don’t assume it’s their internet. Microsoft has confirmed that its September security updates are breaking Always On VPN connections on Windows — the same technology many practices rely on to give staff automatic, encrypted access back to the office network.
This is the kind of problem that looks like a dozen small issues at once: charts won’t load, the practice management system times out, imaging can’t reach the server. Underneath, it’s one cause. Here’s what is happening and how to handle it without opening a hole in your defenses.
What Always On VPN actually does for your practice
Always On VPN is a Windows feature that automatically establishes a secure, encrypted tunnel between a remote computer and your practice network. Unlike an old-fashioned VPN client someone has to remember to launch, it connects on its own the moment the device has internet — which is exactly why it’s popular for remote administrators, a bookkeeper who works from home, or a second location sharing your central server.
That convenience is also why an outage is easy to miss at first. Nobody “forgot to connect.” The tunnel simply fails to form, and every service that depends on the office network fails with it. For a practice handling patient records, that tunnel is not a nicety — it is the encrypted boundary keeping protected health information off the open internet.
What the September updates break
Microsoft has acknowledged that the September cumulative updates for Windows can cause Always On VPN connections to fail after installation. Affected devices install the update normally, then can no longer bring up the VPN tunnel — often with a generic connection error rather than a clear “this update did it” message. Everything else on the machine works, which is what sends people chasing the wrong culprit.
This follows a familiar pattern. Earlier the same month, a separate Windows Server update was breaking Remote Desktop sessions for practices that rely on RDS. When a monthly patch collides with the very tools you use to reach the office remotely, the fix is rarely to stop patching — it’s to patch deliberately.
How to confirm this is your problem
Before you change anything, verify the pattern. A few quick checks separate an update-induced VPN failure from an unrelated network hiccup:
- Timing: Did the failures start right after the September updates installed? Check Windows Update history on an affected device and note the date it applied.
- Scope: Is it only remote or branch users on Always On VPN who are affected, while in-office computers work fine? That points squarely at the tunnel, not the server.
- Consistency: Does the tunnel fail to establish on every attempt, on multiple devices that all received the same update? One machine is a coincidence; several is a pattern.
- Everything-else-works test: Can the affected device browse the web and reach non-VPN resources normally? If yes, the problem is the tunnel, not connectivity.
Document what you find. Knowing which specific update is installed is what lets your IT provider match it to Microsoft’s guidance and choose the right remedy.
Restoring access — the safe way
The dangerous shortcut here is obvious and tempting: turn the VPN off and let people connect “just for today” some other way. Don’t. Exposing a practice-management server or opening remote access without the encrypted tunnel is exactly the kind of gap ransomware crews and credential thieves look for. A one-day workaround becomes a permanent liability.
Instead, work through the options in order of preference:
- Apply Microsoft’s targeted fix. When Microsoft acknowledges an update-caused regression like this, it typically ships an out-of-band fix or a Known Issue Rollback that resolves it without removing your security patches. This is the cleanest path — you keep the protection and regain the tunnel.
- Roll back only if you must, and briefly. Uninstalling the offending cumulative update can restore VPN connectivity, but it also strips out that month’s security fixes. Treat rollback as a short bridge, not a destination, and reapply patches as soon as the corrected update is available.
- Use a secured alternate path in the meantime. If a user genuinely cannot work, route them through another already-hardened, encrypted method rather than a bare connection — and log it, so nothing is left open by accident.
Whatever route you take, this is a good moment to confirm your downtime and business-continuity plan actually covers “remote access is down.” A practice that can keep seeing patients on paper for a few hours is a practice that never has to make a risky security compromise under pressure.
The bigger lesson: patch on purpose, not on autopilot
Two remote-access-breaking updates in a single month is a reminder that fully automatic, immediate patching has a cost. The answer isn’t to delay security updates — unpatched systems are how most breaches start, and this same month’s Patch Tuesday closed hundreds of vulnerabilities, some already being exploited. The answer is a small buffer: let critical updates land on a test or pilot machine first, watch for exactly this kind of regression for a day or two, then roll out to the rest of the practice.
For a busy office, that discipline is hard to maintain in-house. It usually falls to whoever has a spare moment — which means it doesn’t happen consistently, and you find out about a broken tunnel from a frustrated staff member instead of a test bench.
Where Compudent fits
Managing Windows updates so they protect your practice without knocking out remote access is exactly the kind of routine that benefits from a steady hand. Compudent Systems works with dental and medical practices across the GTA and Ontario to keep patching deliberate, remote access secure, and downtime rare. If your Always On VPN has gone quiet this week — or you’d simply like update rollouts handled so surprises like this never reach your front desk — reach out to Compudent for an assessment. Secure remote access should be something you never have to think about.
Sources & further reading:
Related Reading
- The Patch That Locks Out the Front Desk: September’s Windows Server Update Is Breaking Remote Desktop
- A Single Packet, No Password Required: The Actively Exploited Windows IKE Flaw (CVE-2026-33824) and Your Practice
- The Gateway That Lets Your Team In Can Let Attackers In Too: Critical Check Point VPN Flaws (CVE-2026-85102 / 85103) and Your Practice